Both are free. There is no key, no plan and no charge, on either server or
on the API underneath.
Connect
No install. Every client below adds BaseStonk by URL.BaseStonk is not listed in Claude’s connector directory or in ChatGPT’s app
directory. Add it by URL as below.
Claude
One click opens Claude’s Add custom connector dialog with the name and URL filled in:
Or by hand: Settings, Connectors, Add custom connector, then the URL.
Claude Desktop uses the same connectors as Claude on the web. The agent tier
then shows a Connect button that runs the sign-in.
Claude Code
/mcp inside Claude Code, which opens the
same consent page in your browser.
ChatGPT
Settings, Connectors, Advanced, Developer mode, then create a connector with the URL. The agent tier asks you to sign in when it is added.Cursor
In~/.cursor/mcp.json, or .cursor/mcp.json in a project:
Any other client
The transport is streamable HTTP. Every request is aPOST and every
answer is one JSON body; nothing streams. The server keeps no session, so
2025 clients and 2026-07-28 clients both work against the same URL.
Over stdio
The package would be@basestonk/mcp, binary basestonk-mcp. It is not
published on npm yet, so there is no npx or bunx command that works
today. Use the URL.
Read tools
Every tool is annotated read-only, non-destructive and idempotent, and returns typedstructuredContent beside its text, checked against a
declared output schema. chain is base (the default), robinhood or
arc wherever it appears.
token is an address or a ticker such as BSTONK or $GROK. An address
is exact. A ticker that several launches share is not picked for you:
the tool answers with the candidates, marks the official one and any
flagged as impersonating, and asks to be called again by address.
draft_trade’s amount is in units of the pair token, not dollars,
unless the pair is a stablecoin. Fifty on a wtCOIN pair is fifty wtCOIN.
draft_launch refuses a pair that check_pair would refuse, and sends
the pair to the create page as an address, never a ticker. A pair is
permanent after launch. With template, the preset sets the pair and the
taxes; do not pass pair as well.
How to read the answers
- Market caps are fully diluted: price times the whole supply.
null, or “not known” in the text, means unknown. Never read it as zero.- Token amounts carry
raw,decimals,wholeandsymbol. Do arithmetic onrawanddecimals. - Fees are nested and stated as the contract stores them:
burnBpsOfCreatorShareandliquidityBpsOfCreatorShareare shares of the creator’s cut,rewardsBpsOfRemaindera share of what is left. - Dividends are paid in kind, as a basket of other assets.
basestonk://guide/honesty resource holds these rules in full.
The draft loop
A chat app cannot sign. The read server hands the signing to the person and then checks what happened.bsi1_ and carries the draft itself, so nothing is
stored server side. It stops being checked seven days after the draft.
The card
In a host that renders MCP Apps, three tools draw a card:get_token,
draft_launch and draft_trade name ui://basestonk/app.html
(text/html;profile=mcp-app) as their view. A host that does not render
it ignores it and reads the text.
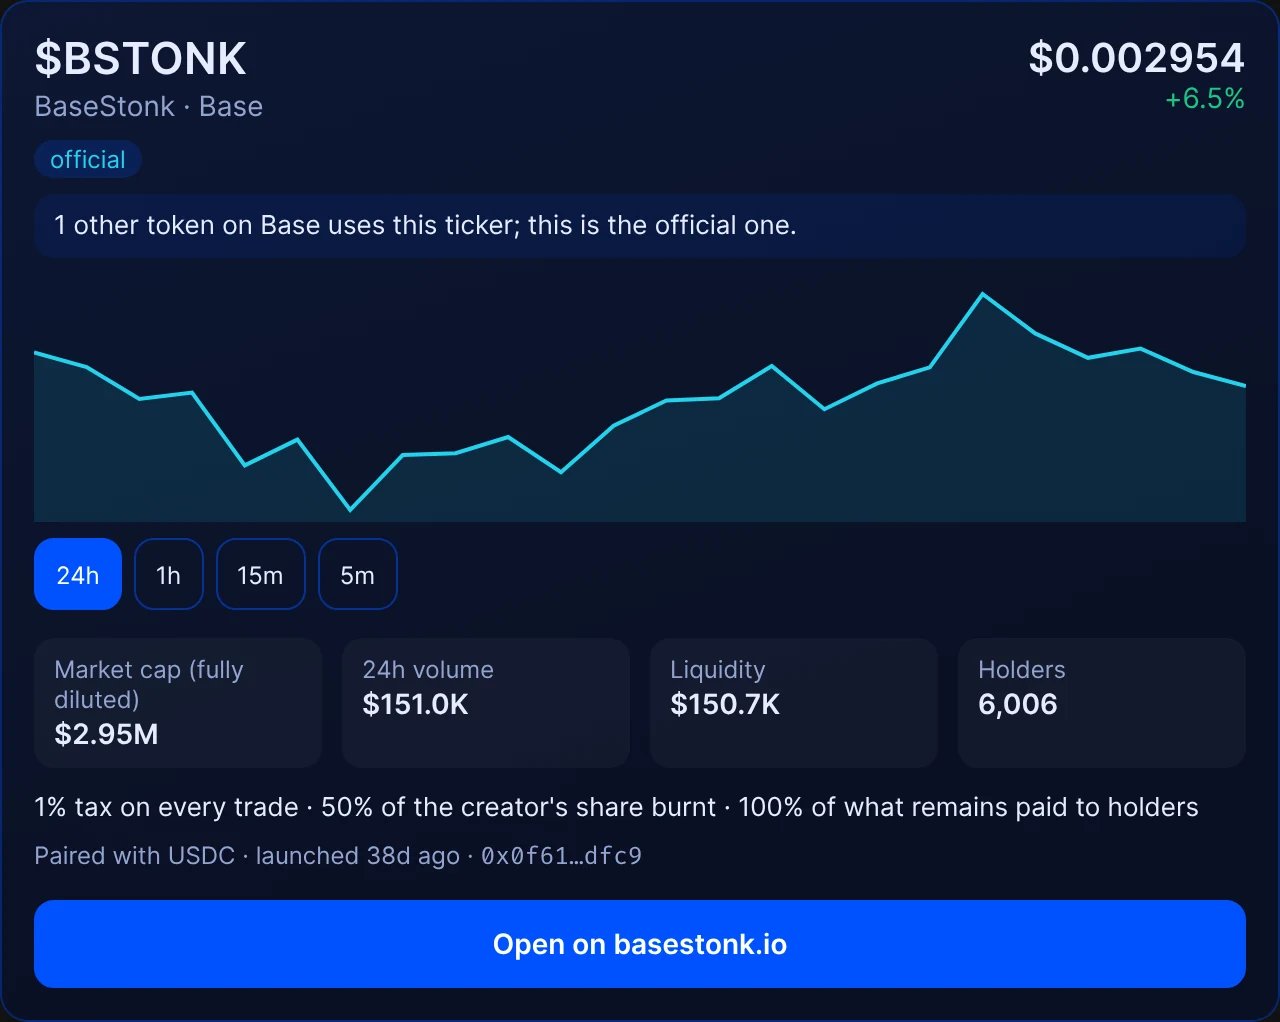
get_token: price, 24h chart with interval tabs, market data, fees
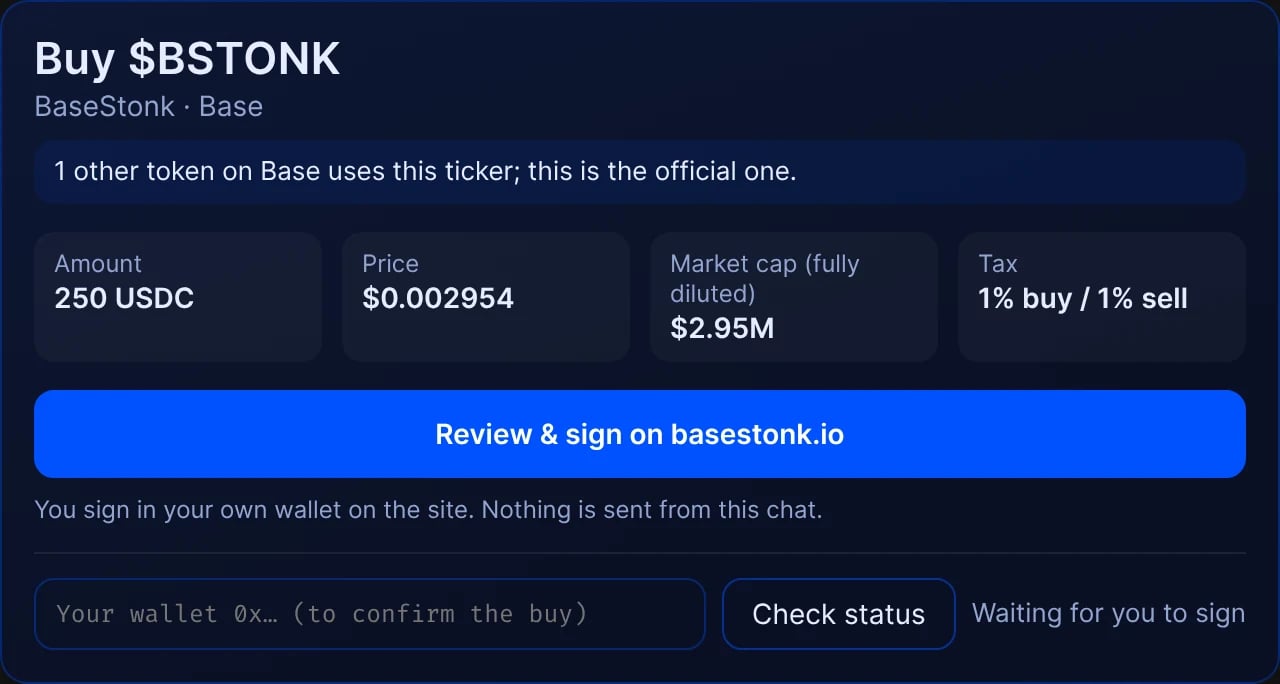
draft_trade: a buy to review, and a status check once it is signed
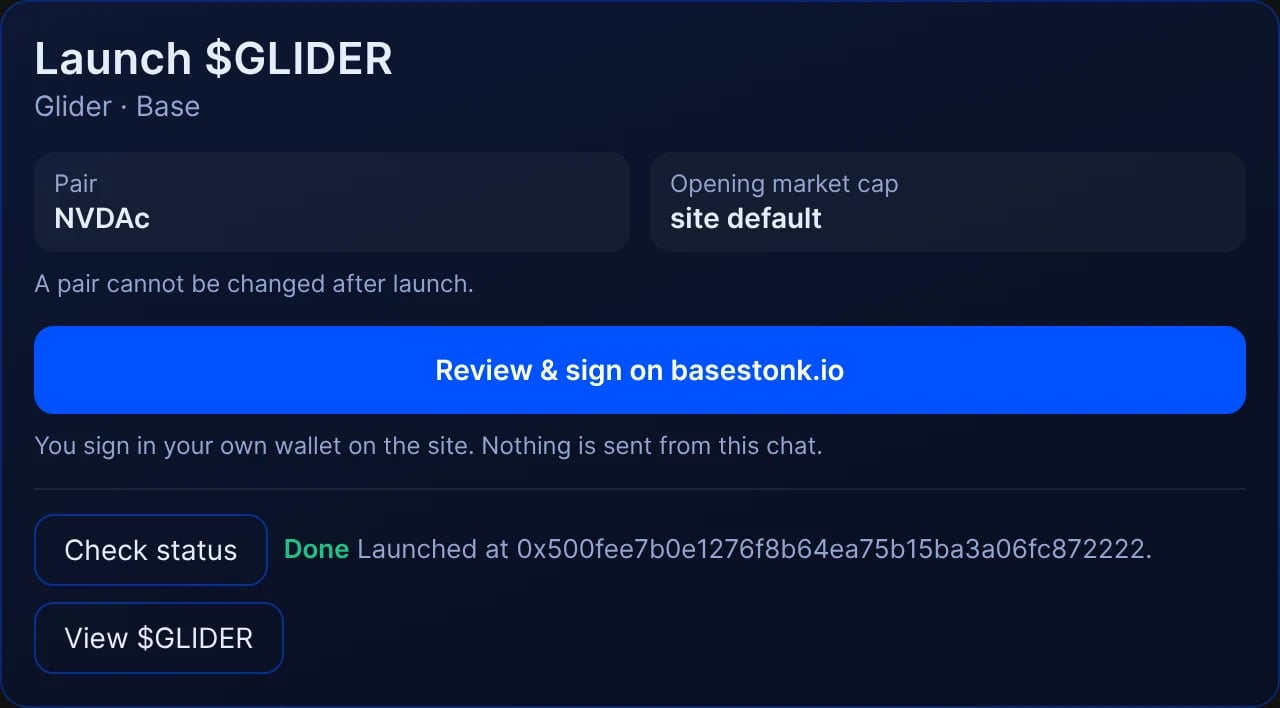
draft_launch after Check status: get_intent found the launch on chain
connectDomains and resourceDomains are both empty);
every number arrives in a tool result. The only tools it calls are
get_candles and get_intent, and it calls them through the host; its
buttons ask the host to open basestonk.io links.
Prompts and resources
Each prompt attaches the honesty guide before its instructions.
The card itself,
ui://basestonk/app.html, is a fifth resource, read by
the host rather than the model.
The server sends cache hints: the tool, prompt and resource lists for ten
minutes, a resource read for ten seconds. On the agent tier the tool list
is marked private, because it names your wallet.
The agent tier
/mcp/agent is the read server plus three tools that act for one wallet.
prepare_launch and prepare_trade are annotated read-only: they read the
chain and return bytes. pin_metadata is not, because it writes a document
to IPFS; it is idempotent, since the same document pins to the same URI.
One source: the OpenAPI document
The agent tools are not a second description of the API. Their inputs are generated from the request bodies of the prepare endpoints inhttps://api.basestonk.io/api/v1/openapi.json. In that document:
- each of the three operations behind them declares its security as
agentBearer(a bearer you minted) oragentOAuthwith thepreparescope (the sign-in below); - sixteen operations carry
x-mcp-tools, naming every MCP tool that calls them.POST /api/v1/agent/launch/preparenamesprepare_launch,trade/preparenamesprepare_trade,agent/metadatanamespin_metadata, and the reads name the read tools built on them.
Sign in
A host that supports MCP authorization, such as Claude or ChatGPT, signs in with a button.- Add
https://api.basestonk.io/mcp/agentas a connector. - The host sends you to
basestonk.io/connect-agent, which names the app and the host it will return you to. - Connect your wallet and approve. The wallet signs
agent:oauthover that app and that one request’s PKCE challenge. The signature works once; nothing else can spend it. - You return to the app, which now holds a token for your wallet.
{"scopes":["read","prepare"]} at POST /api/v1/agent/session
(how), or through
Sign-In with Ethereum with
the prepare scope named in the message, and send it as
Authorization: Bearer <token>.
What the agent can and cannot do
How long it lasts
For client developers
A client identifies itself one of two ways.
An authorization code is single use and lasts 60 seconds. The redirect
carries
code, your state, and iss (https://api.basestonk.io), so a
client can check which server answered.
Signing what an agent prepared
signUrl opens https://basestonk.io/sign#…. The fragment is the
transaction, base64url JSON (v, kind, chainId, from, approvalTx,
tx, expiresAtBlock). A fragment never leaves the browser, so no server
sees or stores it.
The page decodes the payload and checks it before it shows a button:
- the chain must be one BaseStonk runs on
txmust go to a launcher or router the site itself sends to on that chain today (a live launch generation, the live B20 launcher, or the venue router), andkindmust match which it is- the calldata must decode against that contract’s own ABI, and what you are shown is that decoded call, never the agent’s description of it
- an approval must be an ERC-20
approvewhose spender is one of those same contracts, with no value attached
- simulates the first step from the prepared-for wallet before you sign
- refuses to send from any other wallet, or after
expiresAtBlock - sends the approval first, then the transaction, and links the new token after a launch
Limits and errors
The reads a tool makes underneath spend your own API budget,
not a shared one.
prepare_launch and prepare_trade cost 10 units each.
A refused request reaches the model as a tool error, never as an empty
answer:
At the HTTP layer: